GoHighLevel
Is GoHighLevel Secure? Data Privacy and Compliance Guide
Is your client data safe on GHL? We break down GoHighLevel security protocols, HIPAA compliance, and data privacy features to protect your sales funnel.
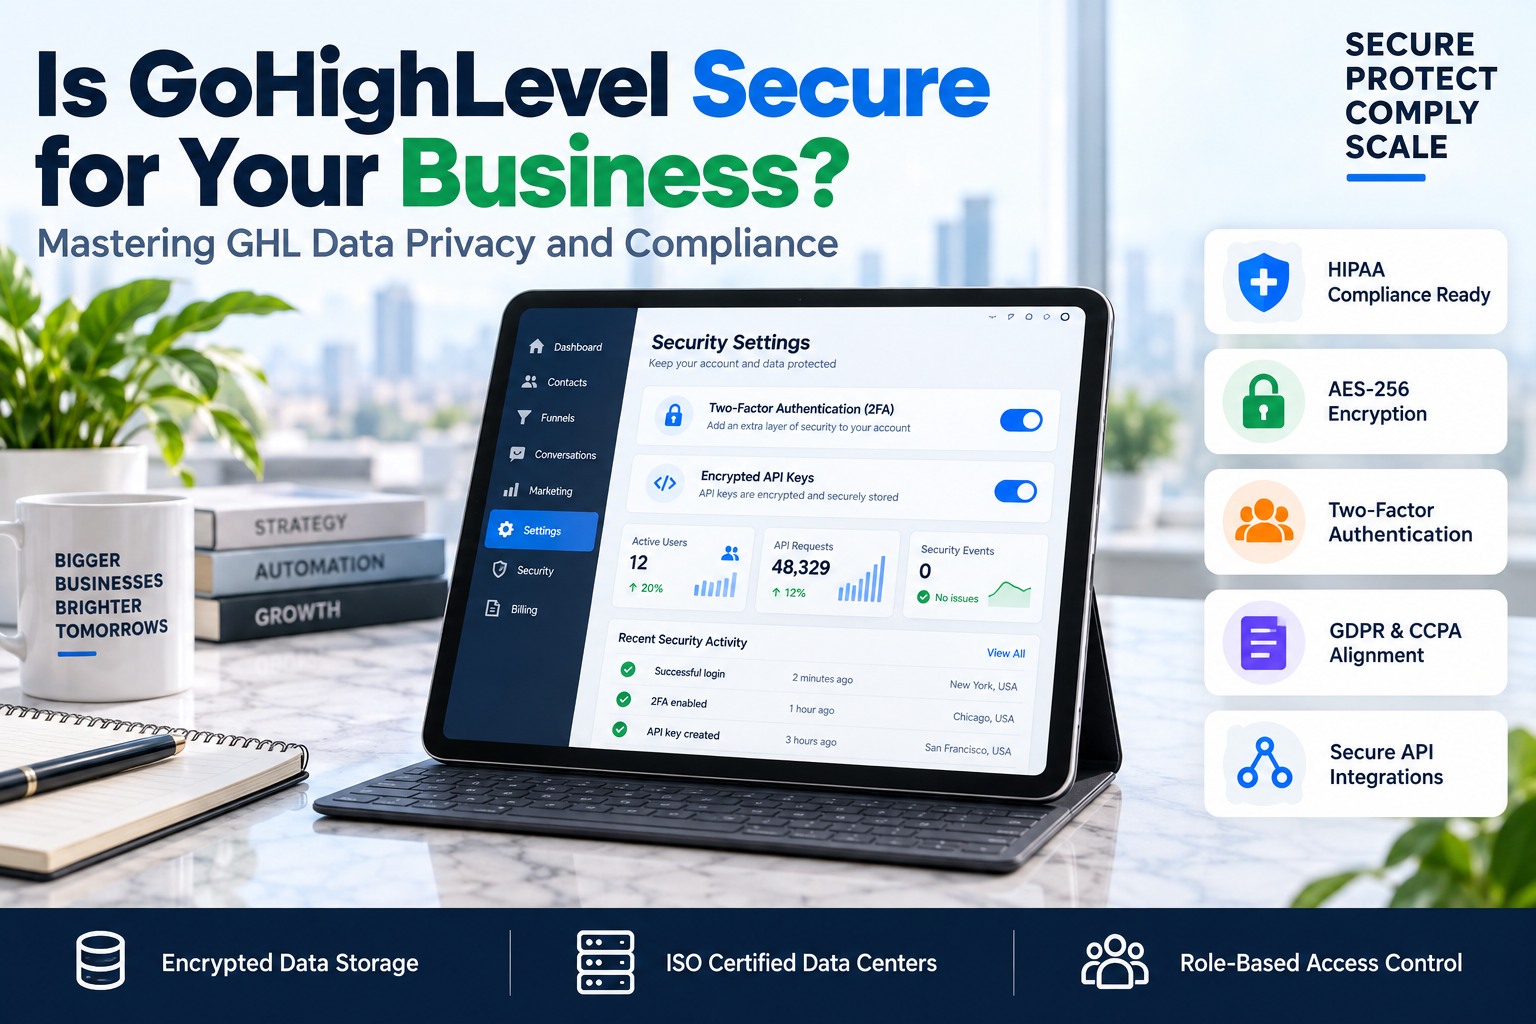
For any coach, agency owner, or B2B consultant, your CRM is the nervous system of your business. It holds your leads, your revenue data, and your intellectual property. The question "Is GoHighLevel secure?" is not just a technical query—it is a fundamental business risk assessment. If a platform fails to protect sensitive client information, your reputation and legal standing are at stake. As GoHighLevel (GHL) continues to dominate the marketing automation space, understanding its security posture is critical before migrating your entire sales funnel.
The Core Architecture: Is GoHighLevel Secure?
GoHighLevel is built on Amazon Web Services (AWS), utilizing one of the most robust and secure cloud infrastructures in the world. By leveraging AWS, GHL inherits a baseline of physical and network security that includes 24/7 monitoring, biometric access controls at data centers, and redundant power systems.
However, software security is a shared responsibility. While AWS secures the infrastructure, GoHighLevel secures the application layer. GHL employs AES-256 encryption for data at rest and TLS (Transport Layer Security) for data in transit. This means whether a lead is filling out a form on your landing page or you are exporting a list of high-ticket clients, the data is encrypted against unauthorized interception.
Data Privacy and Regulatory Compliance
Beyond basic encryption, businesses must worry about specific regulatory frameworks. Is GoHighLevel secure enough to handle regulated data? Let's look at the three big pillars: GDPR, CCPA, and HIPAA.
1. GDPR & CCPA Compliance
For those operating in the EU or California, data privacy is a legal mandate. GoHighLevel provides tools to help users stay compliant, including:
- Data Processing Agreements (DPA): Standardized agreements for users handling EU data.
- Right to Erasure: Tools to easily delete contact records upon request.
- Cookie Consent: Integration capabilities to ensure tracking scripts only fire after user consent.
2. Is GoHighLevel Secure for Healthcare? (HIPAA)
One of the most frequent questions we get at SkyByte is whether GHL is HIPAA compliant. By default, the standard GHL plan is not HIPAA compliant. However, GoHighLevel offers a specialized HIPAA-compliant upgrade. When this is activated, GHL signs a Business Associate Agreement (BAA) with the user, and additional security layers are enabled to protect Protected Health Information (PHI). This makes it a viable solution for medical spas, clinics, and health consultants.
Security Features Every User Should Enable
Security is only as strong as the weakest link, which is often the user account. To ensure your account remains secure, you must utilize the built-in GHL security suite:
- Two-Factor Authentication (2FA): This is the single most effective way to prevent unauthorized access. GHL supports 2FA via email and SMS, ensuring that even if a password is leaked, the account remains locked.
- Role-Based Access Control (RBAC): Not every VA or junior setter needs admin access. Use GHL’s granular permissions to limit access to sensitive billing data or bulk lead exports.
- Audit Logs: You can track which user made what change and when. This transparency is vital for troubleshooting and security audits.
Comparison: GHL Security vs. Competitors
| Feature | GoHighLevel | HubSpot | ClickFunnels |
|---|---|---|---|
| Data at Rest Encryption | AES-256 | AES-256 | AES-256 |
| HIPAA Compliance | Optional Upgrade | Enterprise Only | No |
| Two-Factor Auth | Yes | Yes | Yes |
| Custom Security Roles | Granular | Tiered | Limited |
| AWS Infrastructure | Yes | Yes | Yes |
Safeguarding Your Sales Funnels and Automations
When we build high-conversion sales funnels for our clients, we don't just look at the design; we look at the data flow. A secure funnel requires that your API integrations are handled correctly.
When connecting GoHighLevel to third-party apps via Zapier or Make, you must ensure you are using scoped API keys. This prevents a leak in one system from compromising your entire GHL sub-account. Furthermore, always sanitize your lead capture forms. GHL’s native forms include built-in protection against SQL injection and cross-site scripting (XSS), ensuring that hackers cannot use your landing pages as a backdoor into your CRM.
Common Myths About GoHighLevel Security
Myth 1: "Since it's a 'white-label' platform, it's less secure." White-labeling is purely a branding layer. The underlying security protocols remain managed by the core GoHighLevel engineering team. Your brand name on the URL does not change the encryption level of the database.
Myth 2: "My data is shared with other agencies." GoHighLevel uses a multi-tenant architecture, but data is logically separated. One agency cannot access another agency's data unless explicit permissions are granted via the API or an agency-level user account.
Step-by-Step Security Audit for Your GHL Account
To maximize the answer to "Is GoHighLevel secure?" for your specific instance, follow this 4-step framework:
- Audit Users: Go to Settings > Staff and remove any inactive employees or contractors.
- Enable 2FA: Force 2FA for all admin-level users immediately.
- Review Integrations: Check your 'Labs' and 'Integrations' tab. Revoke access for any third-party apps you no longer use.
- Set Export Restrictions: Turn off the 'Export Contacts' permission for all non-essential staff to prevent data theft.
Frequently Asked Questions
Q: Does GoHighLevel sell my lead data? A: No. According to GHL’s Terms of Service and Privacy Policy, you own your data. GoHighLevel acts as a data processor, not a data owner. They do not sell lead lists or use your data for their own marketing purposes.
Q: Where is GoHighLevel data stored? A: GHL primarily utilizes AWS data centers located in the United States. They use Content Delivery Networks (CDNs) to ensure fast loading times globally while keeping the core database secure.
Q: What happens if I cancel my subscription? A: Upon cancellation, GHL typically retains data for a short grace period before permanent deletion. It is recommended to export your data before closing your account to ensure you maintain your records.
How SkyByte Ensures Your Funnels are Secure
Building a sales funnel isn't just about pretty buttons; it's about building a secure, scalable asset. At SkyByte, we specialize in technical GoHighLevel setups that prioritize both conversion and data integrity. Whether you need a free funnel audit to check your current configuration or a complete system overhaul to fix your problem, we ensure your GHL instance is hardened against threats.
Don't let security concerns stall your growth. A properly configured GoHighLevel account is one of the safest environments for modern B2B lead generation and CRM management. Book a discovery call with SkyByte today to build a high-converting, secure sales engine that protects your most valuable asset: your data.